Develop and implement effective compliance programs. Streamline document-heavy processes with automation, integrated risk assessment and coordinated workflows. Get experienced support from strategy through implementation.
Steve Marshall brings four decades of compliance and internal audit experience, including developing and implementing compliance programs and innovative technical solutions. ICRM connects that experience with the people, processes, controls and governance needed to make a program work in daily operations.
For financial institutions, that means practical support from program design through implementation and improvement. For technology companies, it means helping sell and implement document automation, risk engines and workflow orchestration that fit the client’s compliance needs.
PA / PRACTICAL ADVICE
Sound judgment. A workable path forward.
Practical advice starts with understanding your risks, objectives and operating environment. It combines experienced judgment with evidence about your people, processes, data and technology—then turns that understanding into clear priorities and an achievable implementation path.
The test is whether your team can put the advice to work: who owns each action, what needs to change, how controls will operate and how you will know the changes are effective.
CE / CAPABILITIES THAT ENDURE
Built to adapt. Equipped to remain effective.
Enduring capability is the ability to keep learning, changing and improving. As risks, regulatory expectations, business activities and technology evolve, your program and operating model must evolve with them.
ICRM helps establish the ownership, skills, data, governance and feedback needed to recognize change, reassess decisions and update controls and workflows. What endures is your organization’s ability to respond effectively—not a fixed set of processes or tools.
PA/CE IN PRACTICE
Effective programs. Connected execution.
One approach applied to program development, product design and technology implementation.
PA/CE connects the advice to the outcome. Practical Advice defines the risks, regulatory requirements and results that matter. Capabilities that Endure turns that direction into people, controls, products and workflows that work together—and adapt as conditions change. Our expertise in compliance programs and technology enablement puts this approach into practice.
01 / COMPLIANCE PROGRAMS
Develop. Implement. Improve.
Apply Practical Advice to build a compliance program around actual risk and the three objective categories in COSO’s Internal Control—Integrated Framework: effective and efficient operations, reliable reporting, and compliance with applicable laws and regulations. Steve’s program development, implementation and audit experience connects those objectives with practical policies, accountable ownership, staff capabilities and evidence that controls are working.
Technology is part of that control design. Automated validation, screening, risk rules, approvals and exception handling can perform preventive or detective control activities within the program. Their effectiveness depends on reliable data, appropriate configuration, access and change controls, human oversight and ongoing testing. Capabilities that Endure brings these elements together so the program and its technology can adapt as risks, requirements and business activities evolve.
Program development & implementationDesign the program around actual risk and put it into daily operation
Risk-based policies, controls & governanceConnect requirements to practical controls, accountable ownership and oversight
Training, rollout & effectiveness reviewEquip teams, support implementation and use review findings to improve
Steve helps technology companies align product outcomes with regulatory requirements and the challenges clients face. Client collaboration maps establish what the client does now, what they want to achieve and what they need to resolve the underlying challenge. That shared understanding guides product development, solution positioning and consultative sales, then becomes the basis for a practical implementation scope.
AI implementation starts with a particular need: for example, extracting information from a defined document set, resolving a recurring review bottleneck or supporting a specific risk decision. ICRM helps select an appropriate use case, define success, preserve human review and integrate the solution into existing controls and workflows. Results guide refinement and any decision to expand.
Client collaboration mapsMap current practices, desired outcomes and the needs arising from specific client challenges
Regulatory alignment & product developmentTranslate requirements into intended outcomes, product capabilities and acceptance criteria
Consultative sales & solution alignmentConnect the client’s needs with product capabilities, demonstrate relevant outcomes and set realistic implementation expectations
Focused AI & document automationTarget a defined document or workflow need, with clear outcomes and appropriate human review
Screening & risk enginesConnect screening and assessment outputs with risk-based decisions and review
Workflow & program integrationImplement review, approvals and escalation within the control environment; test outcomes and improve
Connecting objectives, risk, controls and evidence of effectiveness.
Steve’s experience in compliance program development, implementation, internal audit, data governance and technology oversight aligns with the five components of COSO’s Internal Control—Integrated Framework. PA/CE brings that integrated control perspective to practical decisions: define what needs to work, implement it, evaluate the results and adapt.
01
Control environment
Establish accountable ownership, clear roles, oversight and the skills to operate the program.
02
Risk assessment
Connect business and compliance objectives with customer, product, geographic and operational risks; reassess as conditions change.
03
Control activities
Translate requirements into policies, procedures and technology-enabled controls, including approvals, screening, exception handling and escalation.
04
Information and communication
Connect document processing, data quality, risk outputs and reporting so the right people have reliable information for decisions.
05
Monitoring activities
Use program assessments, audit, validation and ongoing review to identify weaknesses, track remediation and improve effectiveness.
The connection is practical: regulatory alignment and product design inform the controls; implementation puts them to work; monitoring and feedback keep the program and its technology responsive to change.
Develop and implement AML/CFT and sanctions compliance programs grounded in your actual risks. Connect risk assessment, policies, controls, customer due diligence, screening, monitoring, training and governance—and help teams put the program into daily operation.
Connect data ownership, quality and controls from initial collection through screening, monitoring and case decisions. Identify where data breaks down and establish practical remediation priorities.
Connect the solution, the buyer and the operating model.
Help technology companies align product outcomes with regulatory requirements and client challenges. Use client collaboration maps to connect current practices, desired outcomes and specific needs—then support product development, consultative sales and focused implementation within the compliance program.
Move information from documents into decisions and action.
Start with a specific client challenge and implement a focused AI or automation use case. Connect document intake, classification or extraction with the risk decisions and workflow steps that need support. Define success, exception handling, human review and decision records before expanding the scope.
Support model risk frameworks, validation planning and effective challenge for financial crime systems. Evaluate the relationship between system design, data, configuration and ongoing performance.
Assess compliance programs and controls, investigate weaknesses and develop achievable remediation plans. Help teams prepare for independent review and respond to findings with clear ownership and evidence.
Program & control assessments
Issue analysis & remediation
Training & stakeholder alignment
PA/CE IN DELIVERY
Assess the fit. Connect the capability.
Two ways ICRM connects advice with effective implementation.
01 / FEASIBILITY & READINESS
Build confidence before committing to implementation.
Establish what works today, what needs to change and whether a proposed solution fits your operating model. Connect the assessment to a business case, an achievable plan and a clear management decision.
Your decision: proceed with a defined scope, address prerequisites or reconsider the solution.
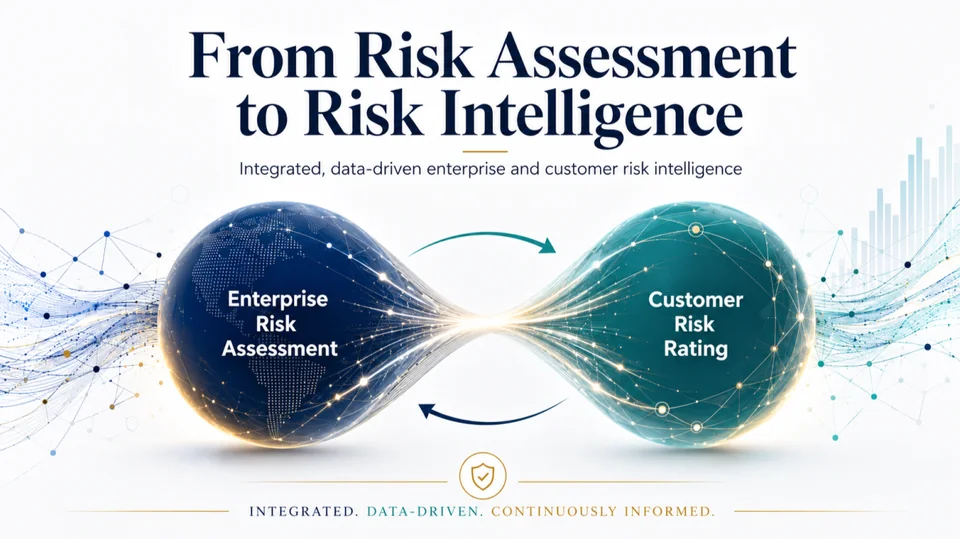
Connect customer risk methodology, ownership information, monitoring and review across the customer lifecycle. Help local teams operate within group standards while addressing jurisdictional requirements.
Your capability: a coherent view of customer risk, supported by explainable decisions and ongoing reassessment.
Bridging the people who manage risk and the people who build the technology.
Develop the program. Make it work in practice.
For banks, insurers and financial services organizations navigating financial crime risk, changing operations and technology decisions.
Develop and implement risk-based compliance programs
Turn policies into customer risk, screening and monitoring processes
Establish data controls, ownership, training and governance
Implement technology and assess ongoing program effectiveness
WHAT’S INVOLVED
Define the need. Put the response to work.
Start with the challenge, your current practices and the outcome you need. ICRM helps establish priorities, agree a practical scope and support the work from design through implementation and ongoing improvement.
Depending on the engagement, deliverables may include a program or control design, a client collaboration map, an implementation roadmap, process and data requirements, training or an effectiveness review.
Whether you are developing a program, addressing a control weakness, evaluating technology or improving a document-heavy process, an initial conversation helps establish where ICRM can help.
Book 30 minutes with Steve or send a brief description of your needs. Together, we agree the scope, deliverables, responsibilities and commercial terms before work begins.
Engagements are scoped to preserve appropriate independence across the first, second and third lines of defense.
EXPERIENCE THAT CONNECTS THE BIG PICTURE TO THE DETAIL.
MEET STEVE MARSHALL
Deep experience. Direct involvement.
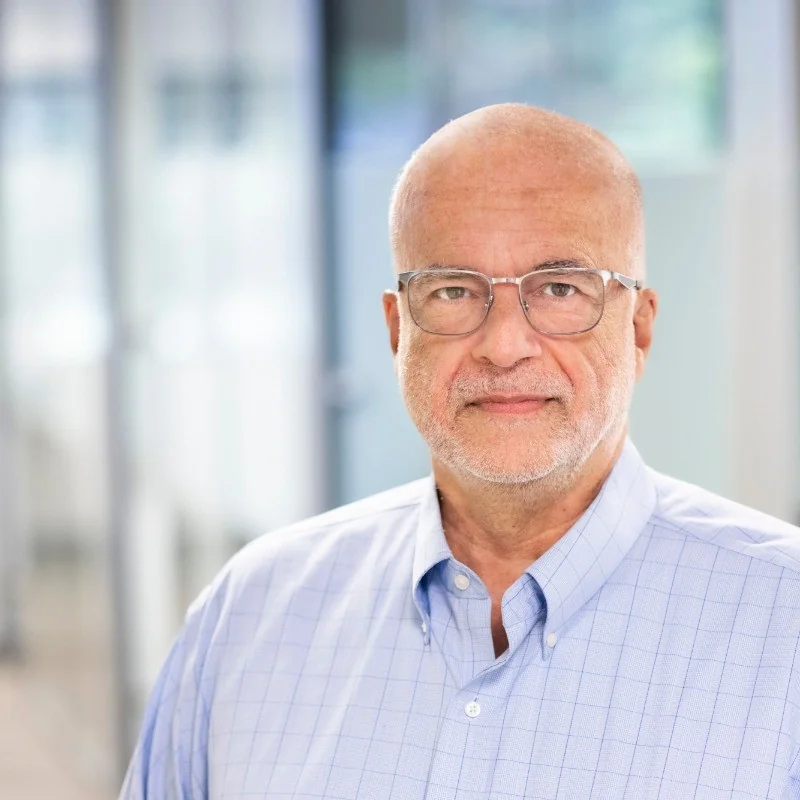
Stephen D. Marshall President, ICRM Services Inc.
Steve brings four decades of compliance and internal audit experience spanning financial institutions and consulting. His work connects financial crime risk management with the data, systems and processes needed to put a program into practice.
His experience includes developing and implementing compliance programs and innovative technical solutions, large-scale sanctions investigations, AML/CFT audits, model risk management and validation, customer due diligence, transaction monitoring and screening, and compliance training.
Through ICRM, Steve helps financial institutions develop and implement effective compliance programs. He also helps technology companies develop, sell and implement solutions whose intended outcomes align with regulatory requirements—integrating document automation, screening, risk engines and workflow orchestration into clients’ compliance programs.
Connecting product capability to program effectiveness.
For a name-screening technology provider, ICRM connected regulatory requirements, product development and the practical needs of financial institutions.